Your home Wi-Fi network is the digital front door to almost everything you do online. Computers, smartphones, security cameras, smart TVs, gaming consoles, voice assistants, and IoT devices may all connect through the same router. If that router or wireless network is poorly secured, an attacker who gains access could potentially misuse your internet connection, target connected devices, or change network settings.
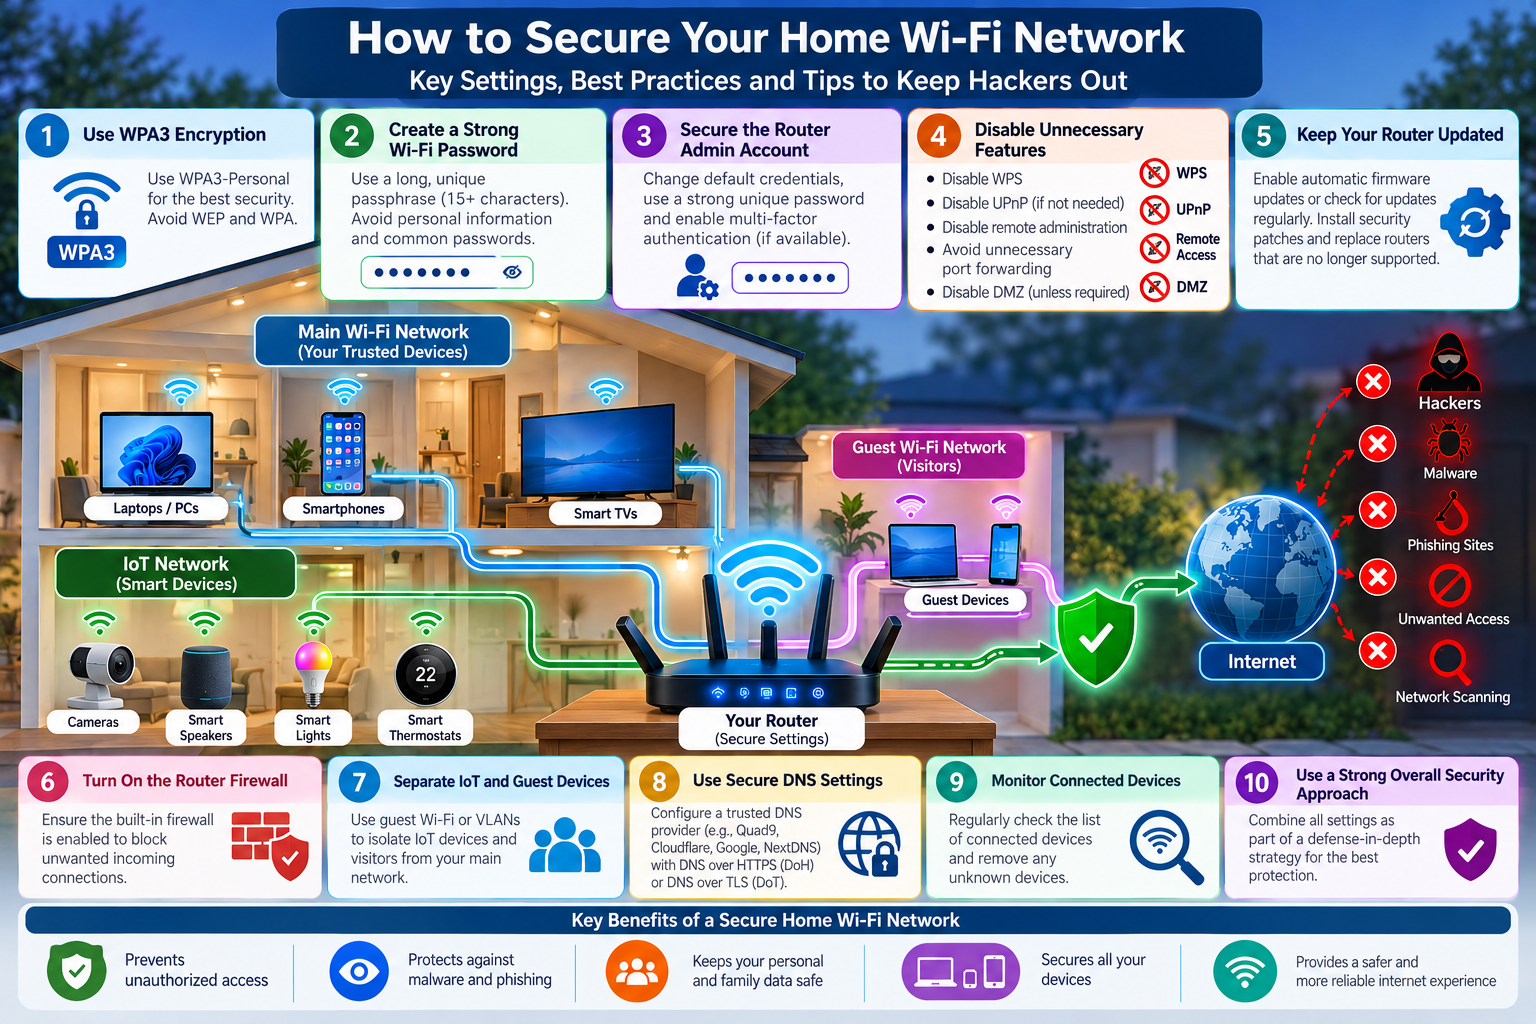
Fortunately, a few carefully chosen settings can significantly strengthen a home network.
1. Use WPA3 encryption
The first setting to check is Wi-Fi security mode. For modern devices, use WPA3-Personal whenever your router supports it. The FTC recommends WPA3 Personal or WPA2 Personal, with WPA3 being the newer option. Avoid legacy WEP and WPA, which no longer provide adequate protection. Consumer Advice
If some older devices cannot connect using WPA3, a WPA2/WPA3 transitional mode may be necessary. If your router supports only WEP or the original WPA even after a firmware update, consider replacing it.
2. Create a strong Wi-Fi password
Your Wi-Fi password should be long, unique, and difficult to guess. Avoid names, addresses, telephone numbers, birthdays, or simple passwords such as HomeWiFi123.
A long random password or passphrase is considerably stronger. For example, use several unrelated words combined with numbers or symbols. The FTC recommends aiming for at least 15 characters when creating passwords. Consumer Advice
Just as importantly, never reuse your Wi-Fi password for email, banking, social media, or other accounts.
3. Secure the router administrator account
Your Wi-Fi password and router administrator password should be different. The administrator account controls critical settings including DNS, firewall rules, wireless security, port forwarding, and firmware.
Change the router’s factory-default administrator credentials immediately. If the router supports multi-factor authentication for its management account, enable it. Disable administration from the internet—often called Remote Administration, Remote Management, or WAN Management—unless you genuinely need it. The FTC specifically recommends disabling remote management. Consumer Advice
4. Disable unnecessary network features
Convenient router features can sometimes increase the attack surface. Unless specifically required, consider disabling:
- WPS (Wi-Fi Protected Setup): Connect devices by entering the Wi-Fi password instead.
- UPnP: Disable it if your applications and devices do not require automatic port configuration.
- Remote administration: Manage the router only from your local network.
- DMZ host: Do not expose a computer or other device directly to the internet unless you understand and require the configuration.
- Unnecessary port forwarding: Remove rules you no longer use.
The FTC recommends turning off WPS, remote management, and UPnP when they are unnecessary. Consumer Advice
5. Keep your router updated
Routers are computers running specialized operating systems, and vulnerabilities can be discovered in their firmware.
Enable automatic firmware/security updates if your router provides the option. Otherwise, periodically check the manufacturer’s support site. Software updates frequently contain security patches that address newly discovered vulnerabilities. Consumer Advice
If your router has reached end-of-support and no longer receives security updates, replacing it should be seriously considered.
6. Turn on the router firewall
Most modern routers contain a built-in firewall that separates your home network from unsolicited connections originating on the internet. Verify that it is enabled. The FTC specifically recommends checking that your router firewall is turned on. Consumer Advice
For most households, avoid manually exposing devices to the internet unless there is a clear reason.
7. Separate IoT and guest devices
Smart cameras, doorbells, televisions, speakers, appliances, and other IoT devices should ideally be separated from computers and devices containing sensitive information.
If your router supports Guest Wi-Fi, VLANs, or IoT network isolation, consider placing IoT devices on a separate network. Guests should similarly use a guest network rather than receiving the password for your primary Wi-Fi.
The FTC recommends separate networks as a way of limiting access between devices—for example, separating security cameras from computers and printers. Consumer Advice
8. Secure your DNS
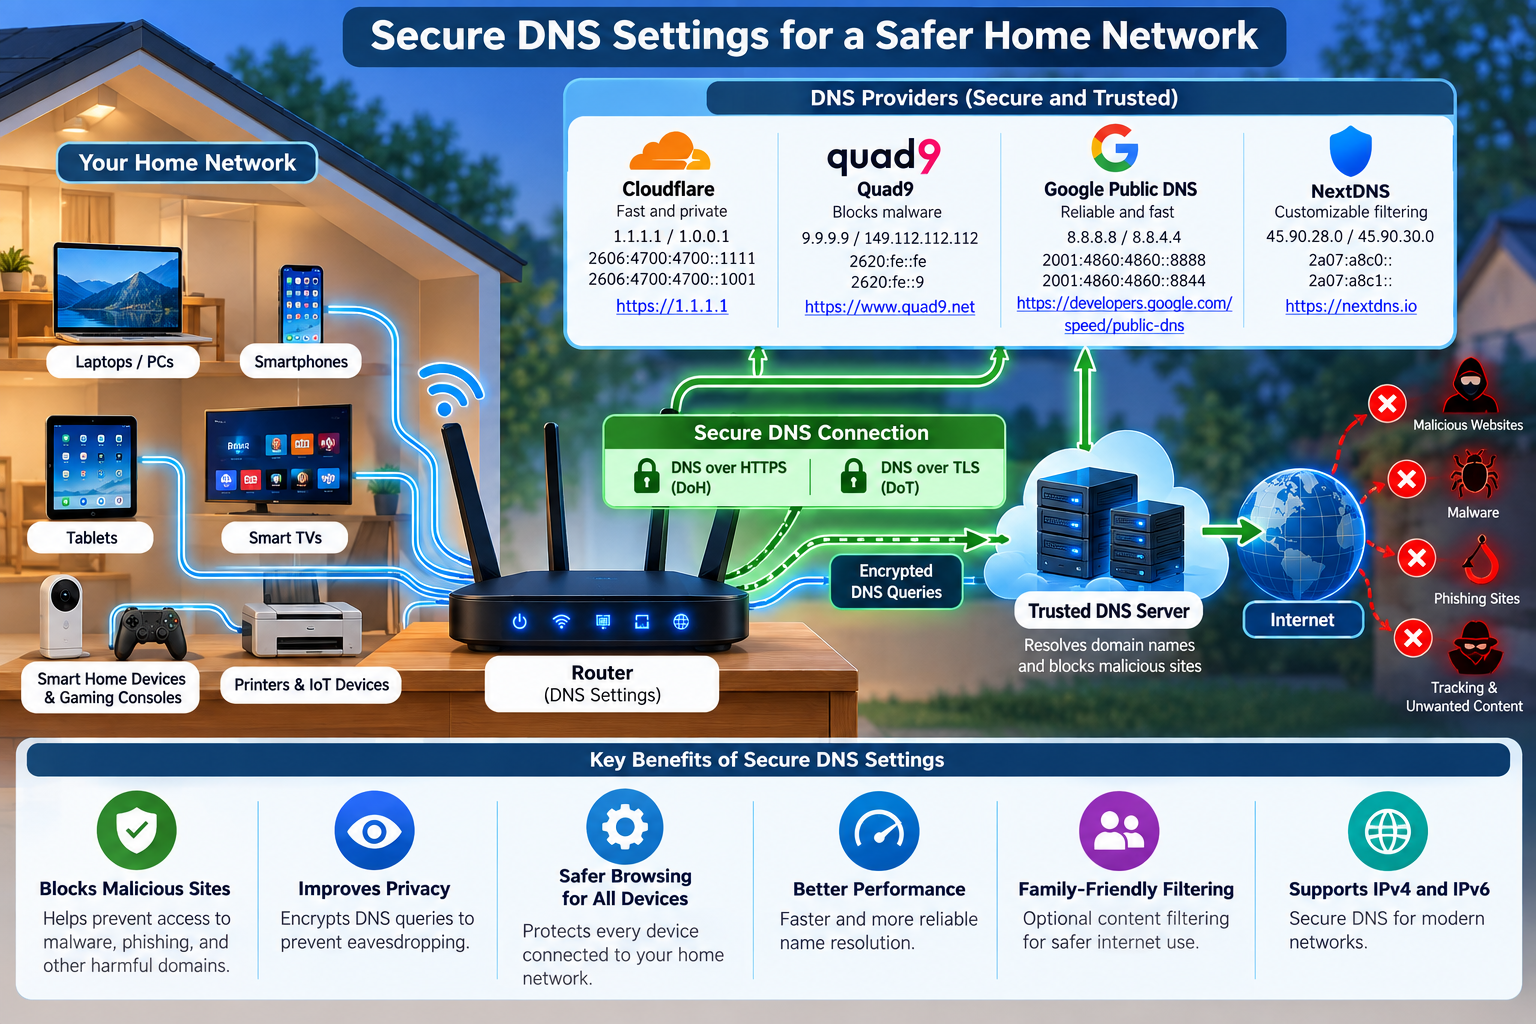
Wi-Fi security should work alongside secure DNS. Configure a trusted DNS resolver such as Quad9, Cloudflare, Google Public DNS, or NextDNS. Where supported, enable DNS over HTTPS (DoH) or DNS over TLS (DoT) and DNSSEC validation.
A security-filtering DNS service can provide another defensive layer by preventing devices from resolving known malicious or phishing domains.
A recommended secure configuration
For a typical modern home, a strong baseline would be WPA3-Personal, a long unique Wi-Fi passphrase, a completely different router-administration password, automatic firmware updates, the router firewall enabled, WPS and remote administration disabled, and separate guest/IoT networks. Add encrypted and security-filtering DNS for another layer of protection.
No home network can be made completely immune to attack. The objective is defense in depth: an attacker should have to overcome several independent security controls rather than exploiting one weak password or poorly configured setting.
Conclusion
Securing your Wi-Fi network does not require becoming a network engineer. A handful of router settings can dramatically reduce unnecessary exposure. Start with strong WPA3 encryption and unique passwords, secure the router’s administrator interface, install firmware updates, disable services you do not need, isolate less-trusted IoT devices, and periodically review the devices connected to your network.
Your router protects the boundary between your digital home and the internet. Secure the router, strengthen the Wi-Fi, and every connected device benefits.
For additional guidance, see the FTC’s guide to securing home Wi-Fi and CISA’s wireless security guidance.